php2shell (CVE-2026-109618, CVE-2026-109619): Frequently asked questions about critical PHP remote code execution vulnerabilities
PHP has released patches for two critical remote code execution vulnerabilities. Fixes are available for PHP 8.2 through 8.5, with source backports for end-of-life PHP 7.4 through 8.1.
Change log
Update October 21: PHP released patches and published its advisories. This post now includes vulnerability details, fixed versions, source backports for end-of-life branches, interim mitigation guidance, updated exploitation details and Tenable product coverage and Vulnerability Watch classification.
Click here to review the change log history
Update October 21: PHP released patches and published its advisories. This post now includes vulnerability details, fixed versions, source backports for end-of-life branches, interim mitigation guidance, updated exploitation details and Tenable product coverage and Vulnerability Watch classification.
October 21: Original publication based on limited public information ahead of PHP's official advisory.
Key takeaways
- CVE-2026-109618 and CVE-2026-109619 are critical vulnerabilities in PHP. The PHP security team rates both CVSSv4.0 9.2 and says they can allow unauthenticated remote code execution.
- Cloudflare reports early attacks emerging, and watchTowr reports exploitation attempts against both vulnerabilities.
- On October 21, 2026, PHP released fixes in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35. End-of-life branches will not receive official releases, but the PHP security team published minimal source backports for PHP 7.4 through 8.1.
Background
Tenable's Research Special Operations (RSO) team has compiled this blog to answer Frequently Asked Questions (FAQ) regarding two critical vulnerabilities in PHP that were announced on October 20, 2026.
FAQ
When were these PHP vulnerabilities first disclosed?
On October 20, 2026, the CVE identifiers circulated on Hacker News and social media. Later that day, the PHP security team published an advance notice of a security release scheduled for October 21 at 14:00 UTC (10:00 AM ET) to address two critical vulnerabilities. The notice said the team could release earlier if details became public or if exploitation appeared in the wild. CERT-EU also published an advisory (2026-018) naming both CVEs. According to the PHP Foundation, the release was originally scheduled for October 22 and was moved up by a day after the CVE identifiers leaked. On October 21, the PHP security team published its security advisory and released patches.
A video shared by researcher Kirill Firsov demonstrates the exploit chain, dubbed php2shell. Firsov credited the video and exploit to researcher LCFR of Calif.io, which has since published a technical writeup. The PHP Foundation credited Calif, OpenAI and Wiz, among others, for their research and responsible disclosure. Calif and Wiz have both said they used AI models in their research.
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.— The PHP Foundation (@ThePHPF) October 20, 2026
What are CVE-2026-109618 and CVE-2026-109619?
| CVE | Description | CVSSv4.0 |
|---|---|---|
| CVE-2026-109618 | PHP Remote Code Execution Vulnerability (OOM Corruption) | 9.2 |
| CVE-2026-109619 | PHP Remote Code Execution Vulnerability (Stale Global State) | 9.2 |
CVE-2026-109618 and CVE-2026-109619 are critical remote code execution (RCE) vulnerabilities in PHP. CVE-2026-109618 stems from how PHP handles out-of-memory (OOM) errors. If memory runs out while PHP's internal request data is only partially initialized, the cleanup that follows can treat that data as valid. CVE-2026-109619 is a use-after-free flaw. Leftover state from one request points to freed memory, and a later request handled by the same worker can then use it. According to PHP, both can be exploited by an unauthenticated remote attacker. PHP's advisory for CVE-2026-109619 also lists memory disclosure as a confirmed impact.
PHP says every installation that serves web requests is at risk, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. PHP considers the risk highest for mod_php, where a demonstrated exploit can be triggered by an unauthenticated request before any application code runs.
CVSS scores differ across sources. The PHP security team rates both vulnerabilities as CVSSv4.0 9.2. According to the PHP Foundation, the CVE identifiers that circulated before the release came with an incorrect CVSS score of 10.0.
Which PHP versions are affected?
According to Calif's technical writeup, the earliest affected code path it found dates to PHP 5.4.0. The PHP security team released the following fixed versions:
| Affected Versions | Fixed Version |
|---|---|
| PHP 8.5.x before 8.5.12 | 8.5.12 |
| PHP 8.4.x before 8.4.27 | 8.4.27 |
| PHP 8.3.x before 8.3.36 | 8.3.36 |
| PHP 8.2.x before 8.2.35 | 8.2.35 |
| PHP 7.4.x through 8.1.x | No official release; minimal source backports from the PHP security team |
| PHP 5.4.x through 7.3.x | End-of-life, no fix from the PHP project |
According to PHP, Linux distributions and LTS vendors received the patches in advance. If you use distribution packages, check your vendor's advisories.
How widespread is PHP, and how many hosts are potentially affected?
According to W3Techs, PHP is used by 69.3% of websites whose server-side language is known. Platforms such as WordPress, Drupal, Joomla, Laravel and Magento all run on PHP. Calif says it confirmed pre-authentication remote code execution against specific versions of popular PHP applications, including WordPress, Drupal, Joomla and Magento. Security researcher Silas Cutler's rough estimate is that over 1.3 million internet-exposed hosts are potentially vulnerable. A Shodan search by Henk Poley counts over 1.9 million internet-exposed hosts running PHP.
Has exploitation been observed in the wild?
On October 21, Cloudflare CTO Dane Knecht said the company is "seeing early attacks emerging" and is updating its mitigations as new attack vectors appear. watchTowr says it has reproduced both vulnerabilities and is observing exploitation attempts against both.
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.— Dane Knecht 🦭 (@dok2001) October 21, 2026
Is there a proof-of-concept (PoC) available?
Code claiming to exploit these vulnerabilities is circulating publicly, but we have not verified that any of it works against CVE-2026-109618 or CVE-2026-109619. Unverified exploit code is sometimes laced with malware, so treat it with caution. The PHP Foundation said the PHP security team inspected PoCs that appeared after the leak but "did not identify any functional exploits at the time of release/public disclosure."
Are patches or mitigations available?
Yes. The PHP security team released fixed versions on October 21 (see the table above). For end-of-life branches, it published minimal source backports for PHP 7.4 through 8.1, for those who build from source. If you run another end-of-life version, upgrade to a supported release or ask your distribution or LTS vendor.
The PHP security team says updating is the only complete fix. For organizations that cannot update immediately, PHP's advisory lists configuration changes that reduce exposure to specific attack paths but do not make an installation safe. For CVE-2026-109618, PHP lists setting memory_limit=-1 in a way applications cannot override. For CVE-2026-109619, it lists setting session.upload_progress.enabled=0 and, on PHP 8.5, fatal_error_backtraces=0. PHP says to restart every PHP worker after these changes. PHP also suggests a container or cgroup memory limit as an availability boundary, though it says this is not a complete mitigation either.
CERT-EU also recommends that organizations that cannot update right away consider isolating internet-facing applications from public networks until a fix is applied and verified.
Cloudflare has deployed WAF rules for the known exploit vectors, available to all customers including the free tier. Cloudflare describes this as a stopgap only. The rules only cover traffic routed through Cloudflare.
Have PHP vulnerabilities been exploited before?
Yes. The CISA Known Exploited Vulnerabilities (KEV) catalog includes three vulnerabilities in PHP itself. Two of them are known to have been used in ransomware campaigns:
| CVE | Product | Added to KEV | Ransomware Use | Tenable Blog |
|---|---|---|---|---|
| CVE-2024-4577 | PHP (CGI) | 2024 | Known | CVE-2024-4577: Proof of Concept Available for PHP-CGI Argument Injection Vulnerability |
| CVE-2019-11043 | PHP-FPM | 2022 | Known | CVE-2019-11043: Vulnerability in PHP-FPM Could Lead to Remote Code Execution on nginx |
The third, CVE-2012-1823, is a PHP-CGI flaw that CVE-2024-4577 later bypassed.
Has Tenable Research classified these vulnerabilities as part of Vulnerability Watch?
Yes. CVE-2026-109618 and CVE-2026-109619 have been classified as “Vulnerability of Concern” as part of Vulnerability Watch.
Is Tenable affected by these vulnerabilities?
Tenable is aware of these vulnerabilities. For updates, please visit trust.tenable.com.
Has Tenable released any product coverage for these vulnerabilities?
The following Tenable Web App Scanning plugins are available for these vulnerabilities:
| Plugin ID | Name |
|---|---|
| 115719 | PHP 8.5.x < 8.5.12 Multiple Vulnerabilities |
| 115720 | PHP 8.4.x < 8.4.27 Multiple Vulnerabilities |
| 115721 | PHP 8.3.x < 8.3.36 Multiple Vulnerabilities |
| 115722 | PHP 8.2.x < 8.2.35 Multiple Vulnerabilities |
The following Tenable plugins are available to identify PHP installations and unsupported versions on affected systems:
| Plugin ID | Name |
|---|---|
| 48243 | PHP Version Detection |
| 58987 | PHP Unsupported Version Detection |
| 200476 | PHP Scripting Language Installed (Windows) |
| 216936 | PHP Scripting Language Installed (Unix) |
A list of Tenable plugins for these vulnerabilities can be found on the individual CVE pages for CVE-2026-109618 and CVE-2026-109619 as they're released. These links will display all available plugins for these vulnerabilities, including upcoming plugins in our Plugins Pipeline.
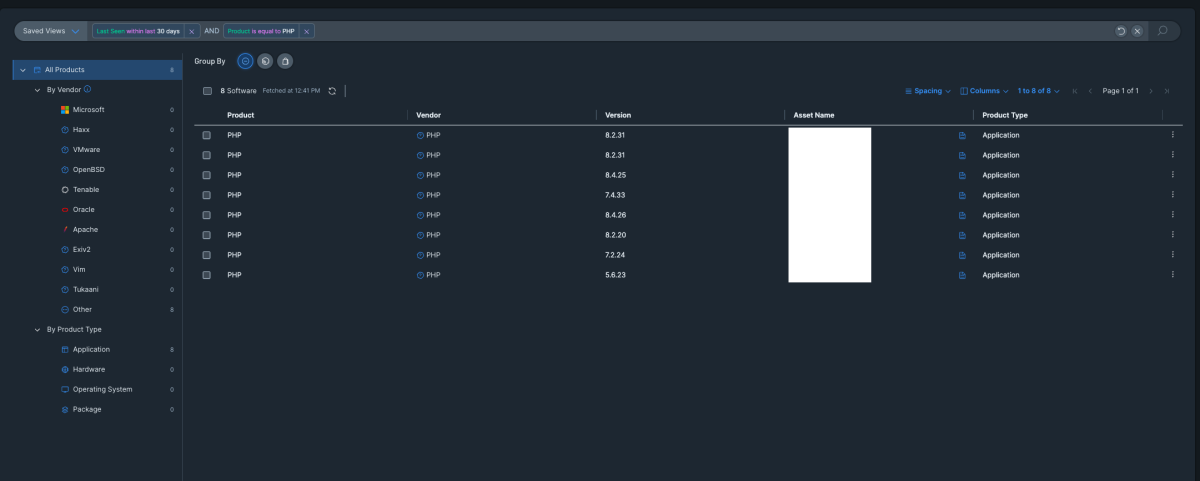
Tenable One Vulnerability Management customers can use the Software tab in Explore to find assets running PHP. Filter by Product is equal to PHP, then compare each asset's PHP version against the fixed versions above. The tab is populated from scan results, so run credentialed or agent scans regularly to keep it current.
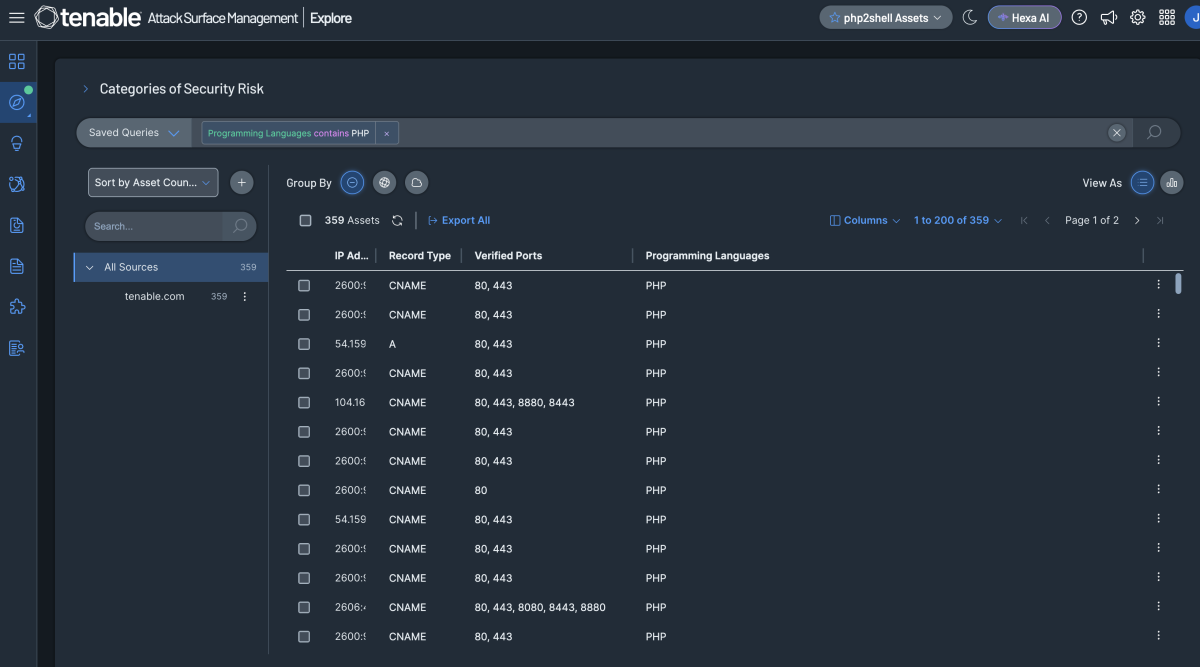
Customers can also use Tenable Attack Surface Management to find public-facing assets running PHP with this query: Programming Languages contains PHP.
Get more information
- PHP Foundation on X: Advance notice of upcoming security release
- PHP.net Security Advisory: Critical remote code execution vulnerabilities
- PHP GitHub Advisory GHSA-w8hw-w9fx-j79w: RCE via OOM corruption (CVE-2026-109618)
- PHP GitHub Advisory GHSA-6wmf-4rv5-p3rp: RCE via stale global state (CVE-2026-109619)
- PHP Foundation: Today's PHP security release and how we're strengthening PHP security
- Calif: php2shell technical writeup
- CERT-EU Security Advisory 2026-018
Join Tenable's Research Special Operations (RSO) Team on Tenable Connect for further discussions on the latest cyber threats.
Learn more about Tenable One, the Exposure Management Platform for the modern attack surface.
Learn more
Learn more
Related articles
- Exposure Management
- Vulnerability Management
Tenable One
Request a demo
The world’s leading AI-powered exposure management platform.
Thank You
Thank you for your interest in Tenable One.
A representative will be in touch soon.
Form ID: 7469
Form Name: one-eval
Form Class: c-form form-panel__global-form c-form--mkto js-mkto-no-css js-form-hanging-label c-form--hide-comments
Form Wrapper ID: one-eval-form-wrapper
Confirmation Class: one-eval-confirmform-modal
Simulate Success